Series · 8 parts · 89 min total
Workload Identity
No static keys, anywhere: give every pod, VM and AI agent its own short-lived identity on AWS, Google Cloud and Azure, then federate across clouds.
Start reading →Inside one cloud
- 01
EKS: Pod Identity vs IRSA · Security
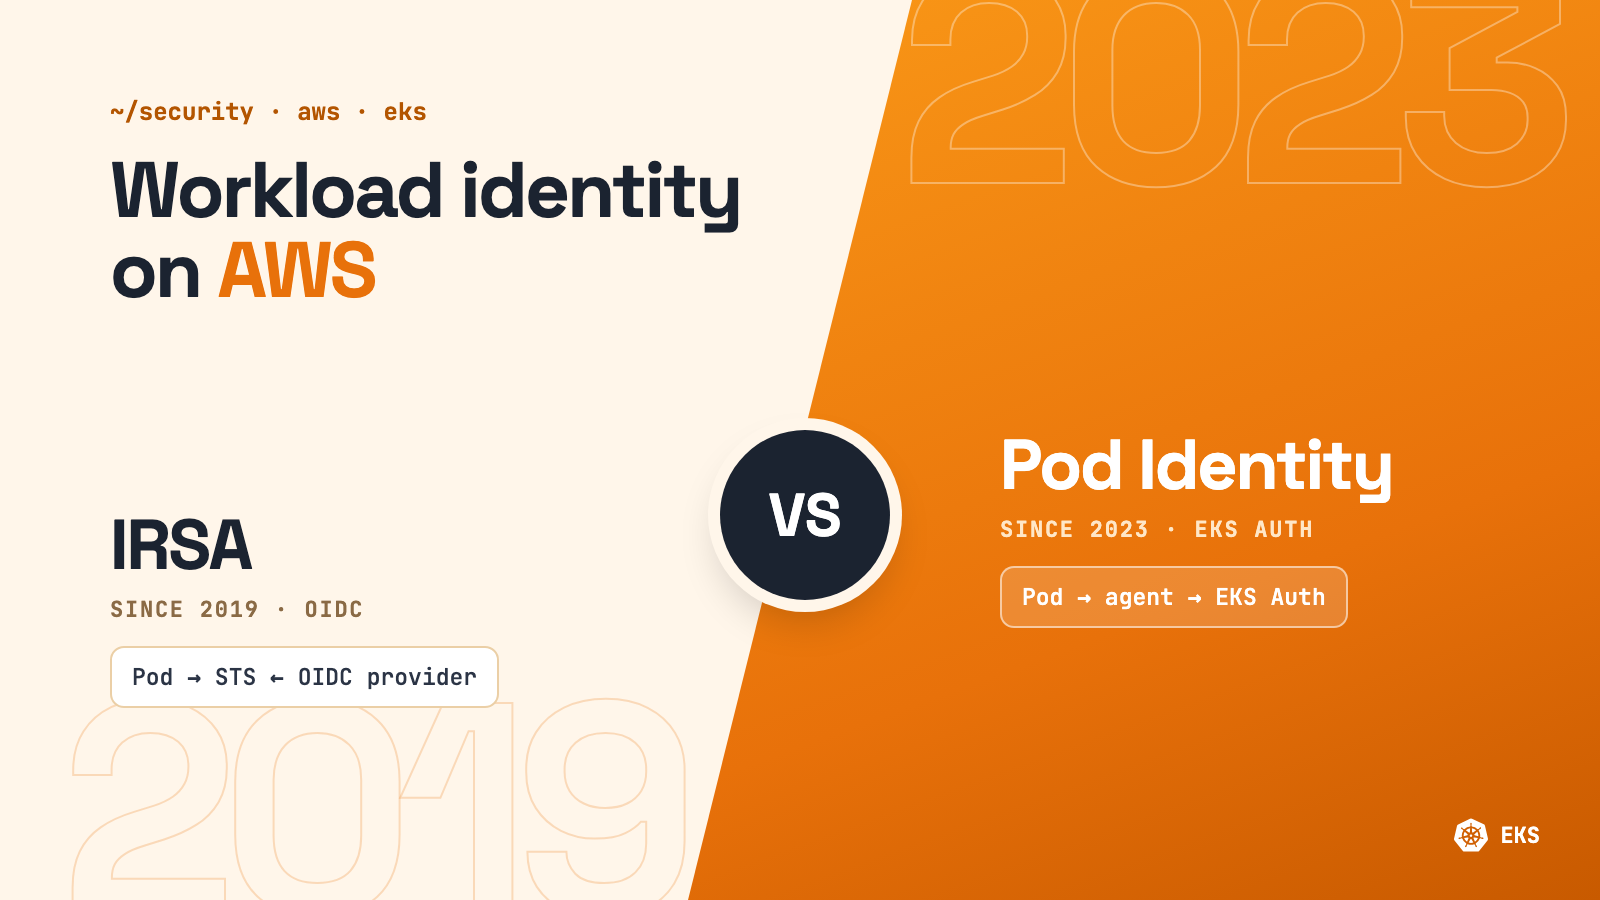
Workload identity on AWS: EKS Pod Identity vs IRSA
How pods get AWS credentials without static keys — how IRSA and EKS Pod Identity work under the hood, where they differ, and how to migrate safely.
- 02
GKE Workload Identity · Security
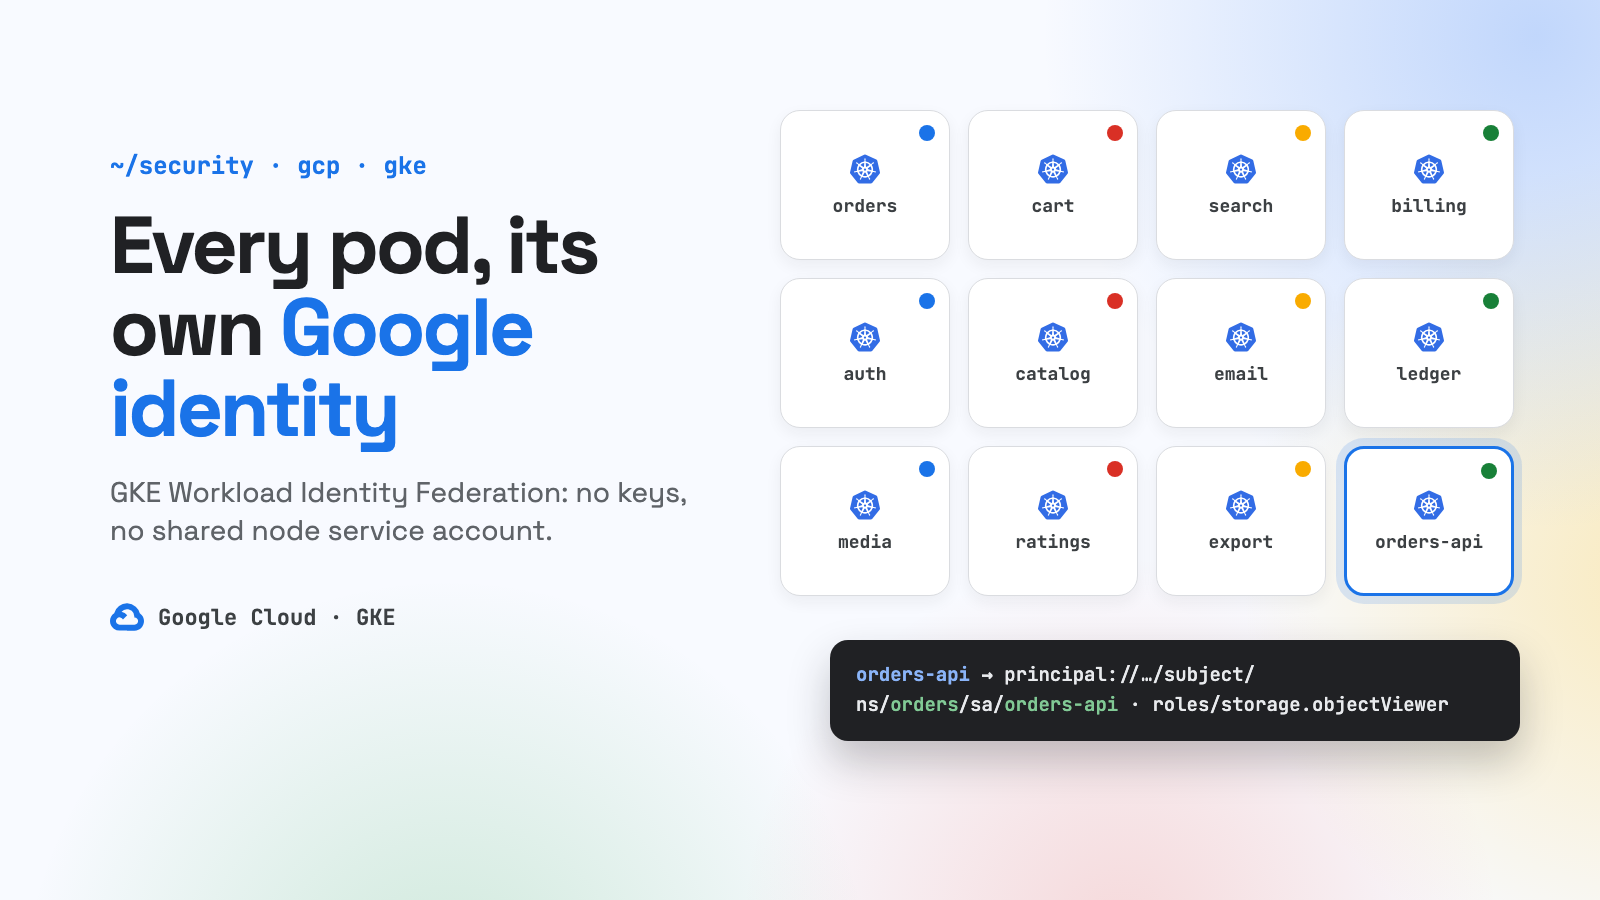
Workload Identity on GKE: give every pod its own Google identity
A practical guide to Workload Identity Federation for GKE: direct principal access vs linked service accounts, gcloud and Terraform setup, verification, cross-project access, gotchas, and managing it as YAML with Config Connector.
- 03
AKS: Entra Workload ID · Security
Workload Identity on Azure: Microsoft Entra Workload ID for AKS, from az CLI to GitOps
Give every AKS pod its own Azure identity without client secrets: how Entra Workload ID works, step-by-step setup with az CLI and Terraform, Key Vault CSI, scaling past 20 federated credentials, and managing it all from the app's Helm chart with Azure Service Operator.

Across clouds
- 04
AWS → Google Cloud · Security
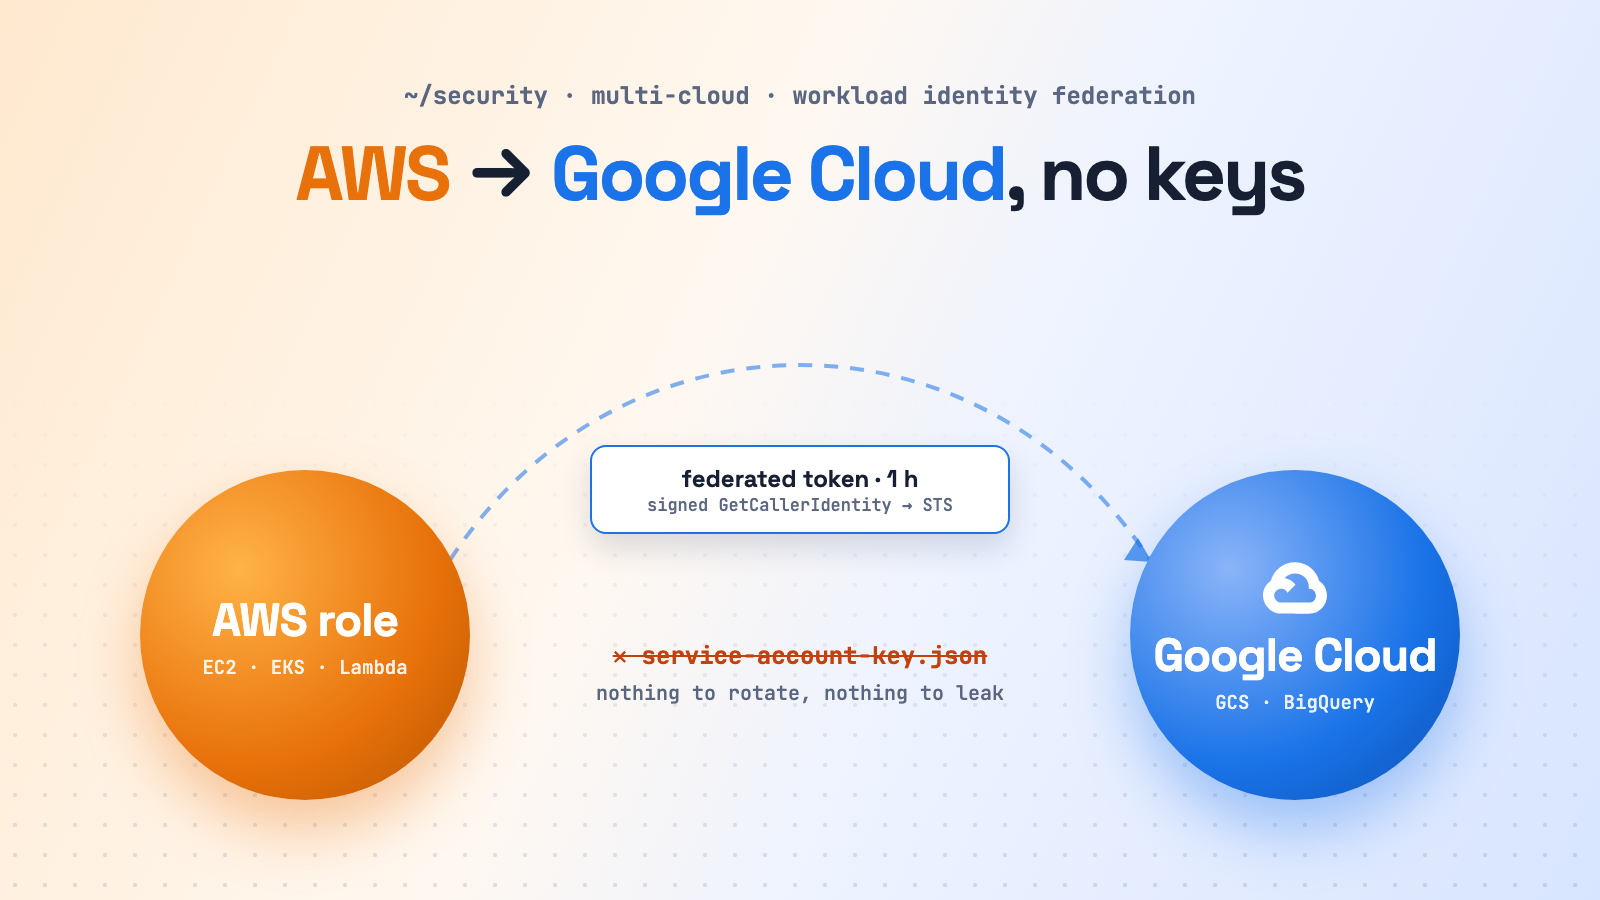
Workload Identity Federation from AWS to Google Cloud — without service account keys
Let EC2, Lambda, ECS and EKS workloads call Google Cloud with short-lived tokens: how the token exchange works, step-by-step setup, the EKS trap, and a hub-and-spoke design for many accounts.
- 05
AWS → Azure · Security
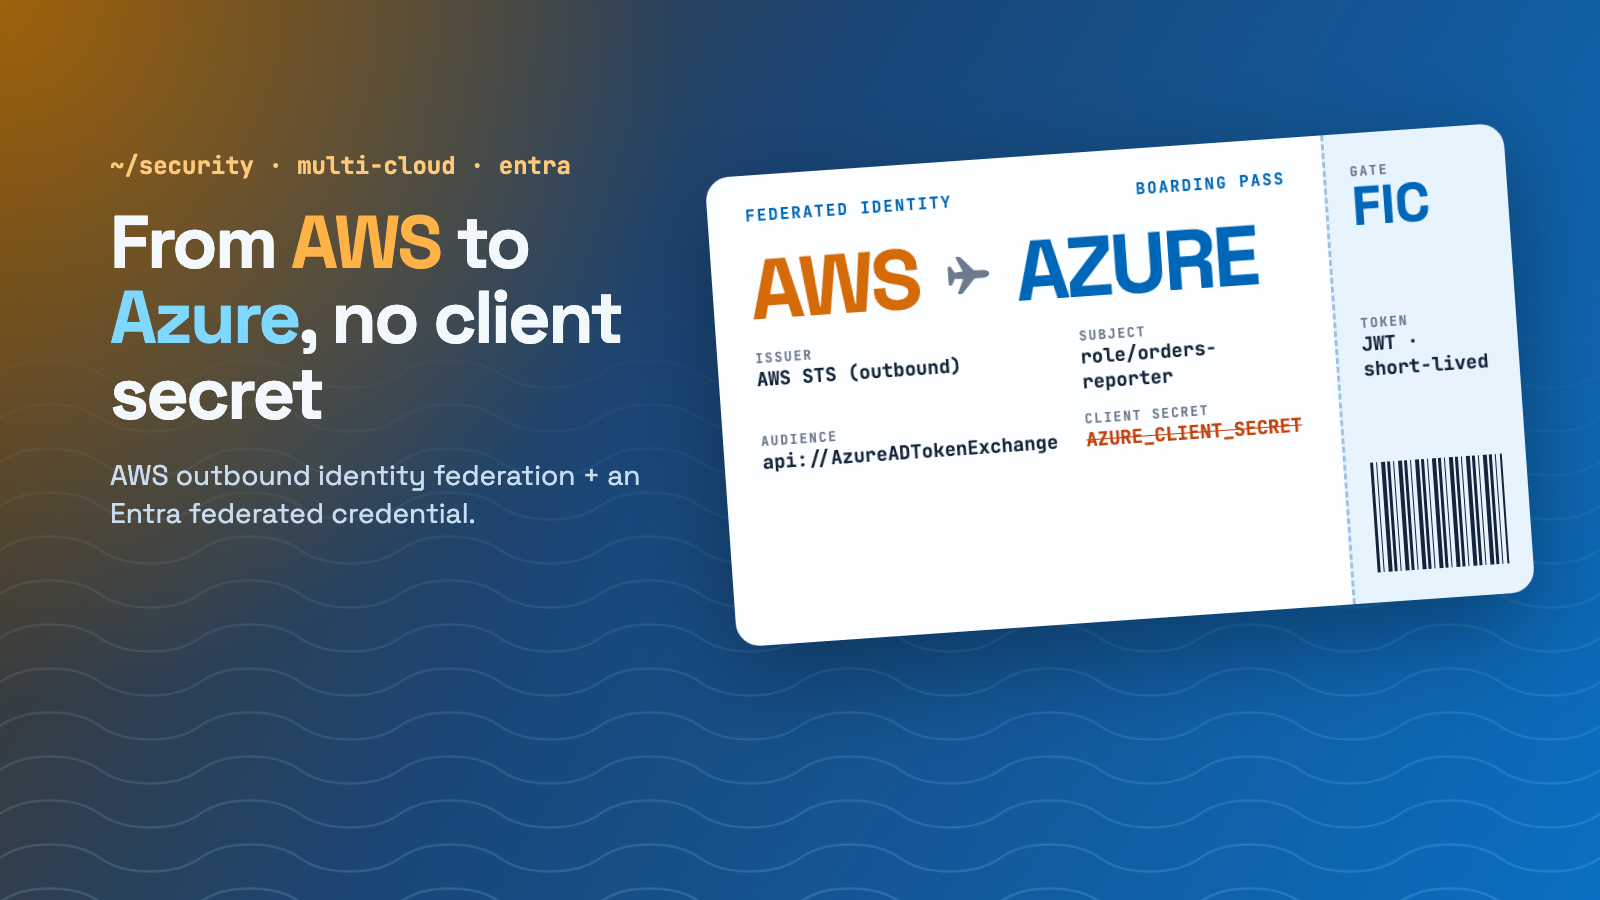
Workload Identity Federation from AWS to Azure — no client secrets
Let EC2, Lambda, ECS and EKS workloads call Azure with short-lived tokens: AWS IAM outbound identity federation, Entra federated credentials on managed identities, the EKS shortcut, and a hub-and-spoke design.
- 06
Google Cloud → AWS · Security
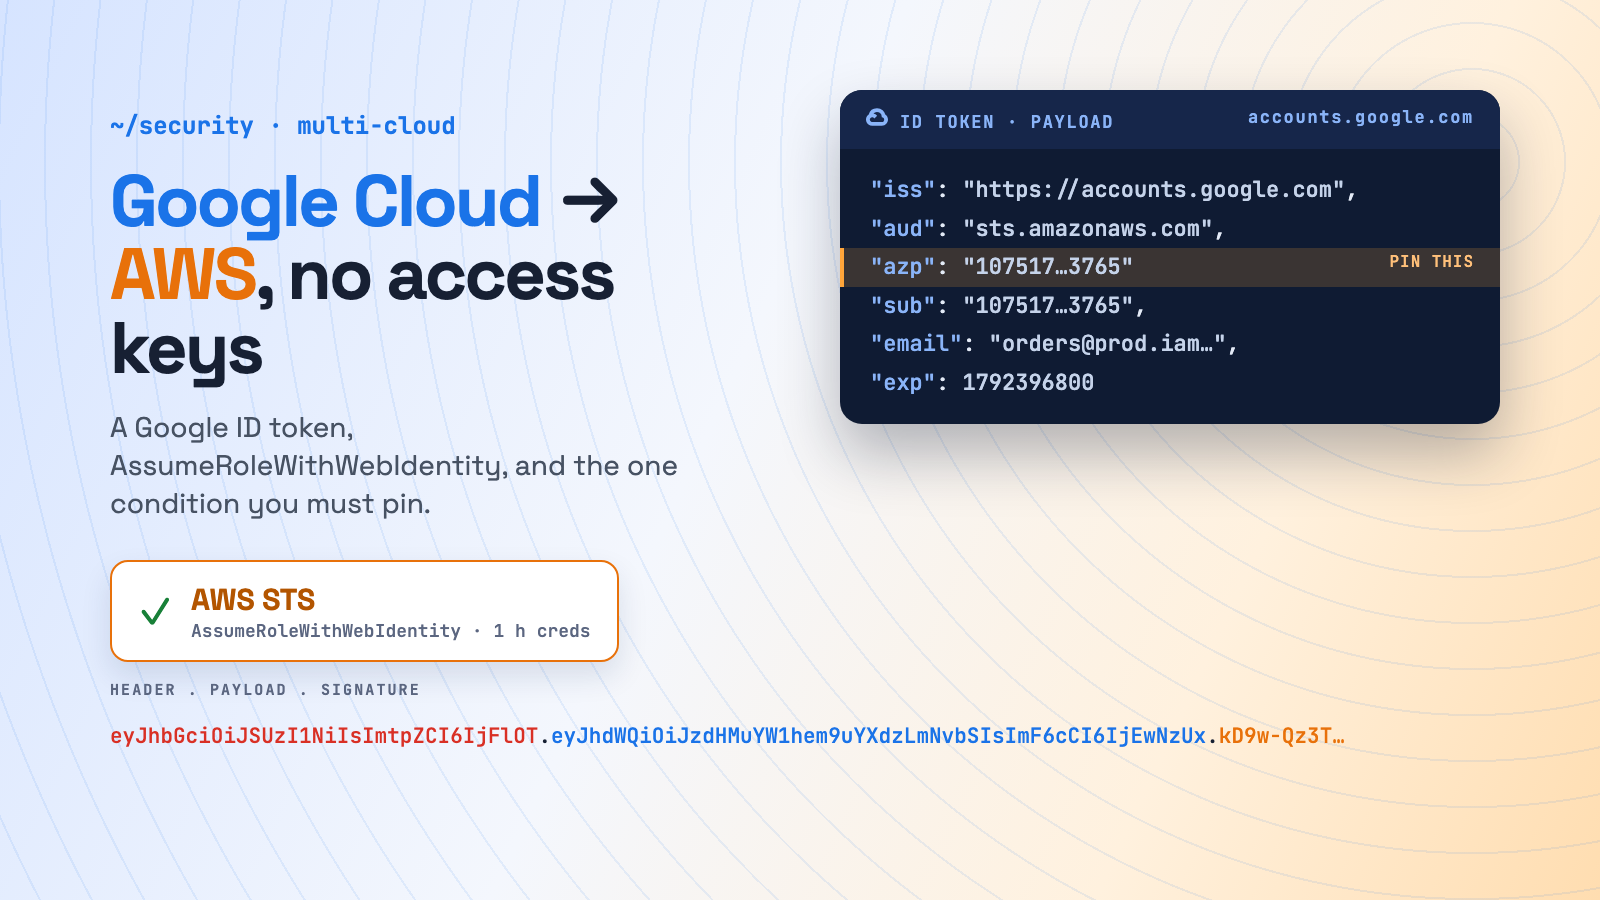
Workload Identity Federation from Google Cloud to AWS — no access keys
Let GCE, Cloud Run, Cloud Functions and GKE workloads call AWS with temporary credentials: Google ID tokens and AssumeRoleWithWebIdentity, the trust-policy mistake that opens your role to the whole internet, the GKE OIDC path, and Terraform for both sides.
Beyond the cloud
- 07
IAM Roles Anywhere hub · Security
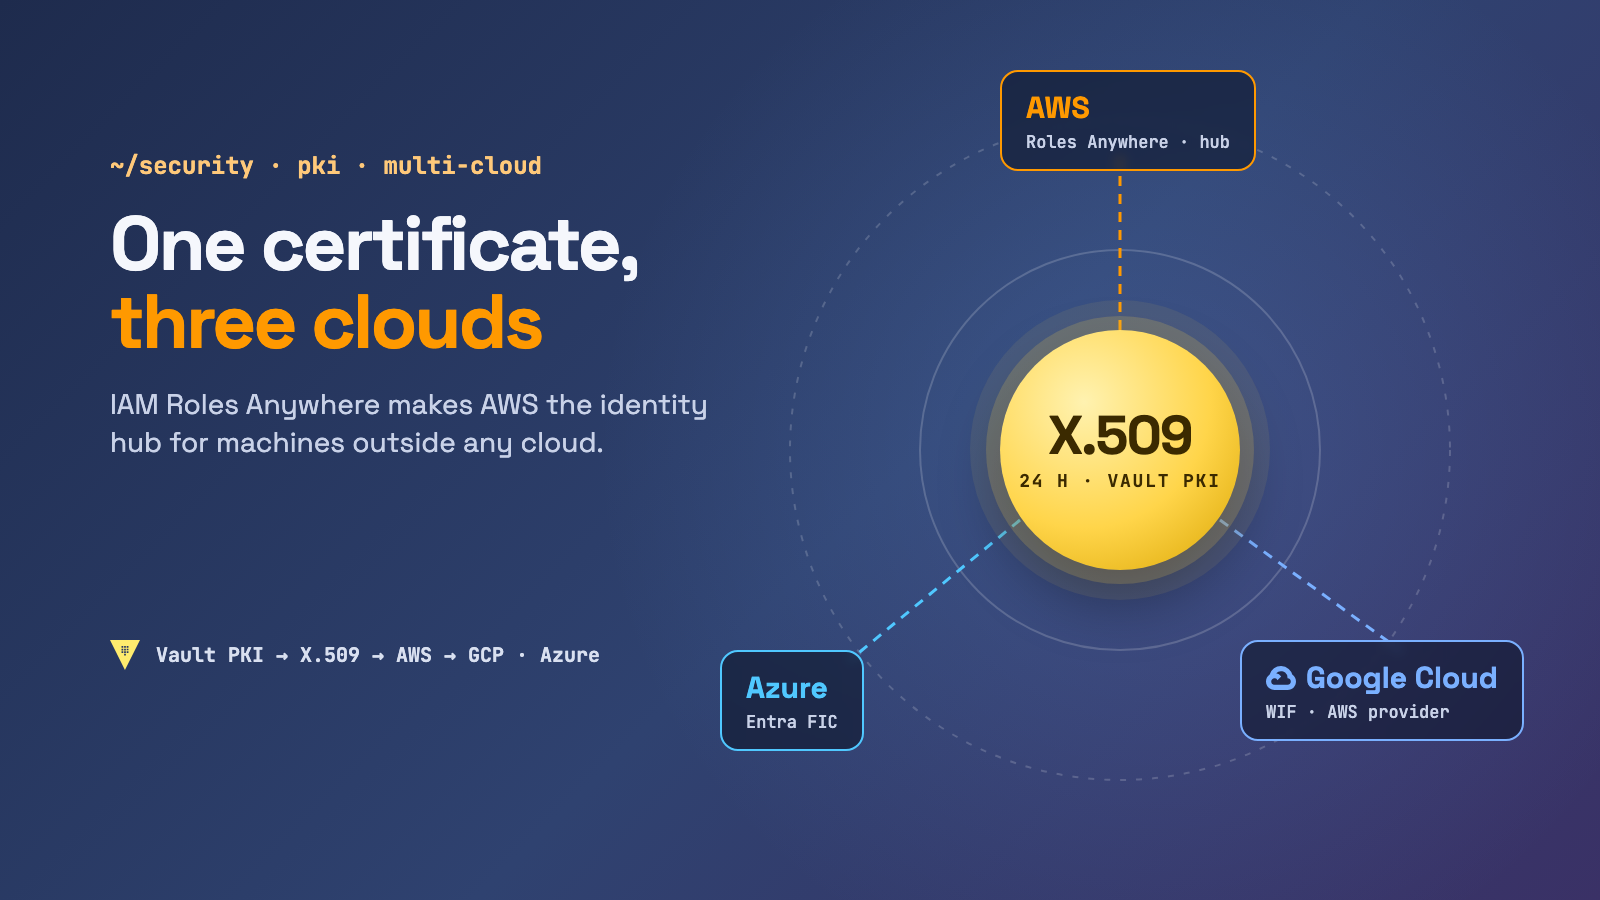
IAM Roles Anywhere: AWS as the identity hub for on-prem workloads into AWS, Google Cloud and Azure
Give machines with no cloud identity — on-prem VMs, edge devices, self-hosted CI — short-lived X.509 certificates from Vault PKI, turn them into AWS role sessions with IAM Roles Anywhere, and federate onward to Google Cloud and Azure without a single static key.
- 08
Identity for AI agents · Security
Identity for AI agents: workload identity, delegation and MCP authorization without shared keys
Workload identity tells you which pod is calling. AI agents need more: on whose behalf they act, and what they may do right now. A practical guide to agent identity with RFC 8693 token exchange, the MCP authorization spec, token vaults, and the managed options on AWS, Google Cloud and Microsoft Entra.